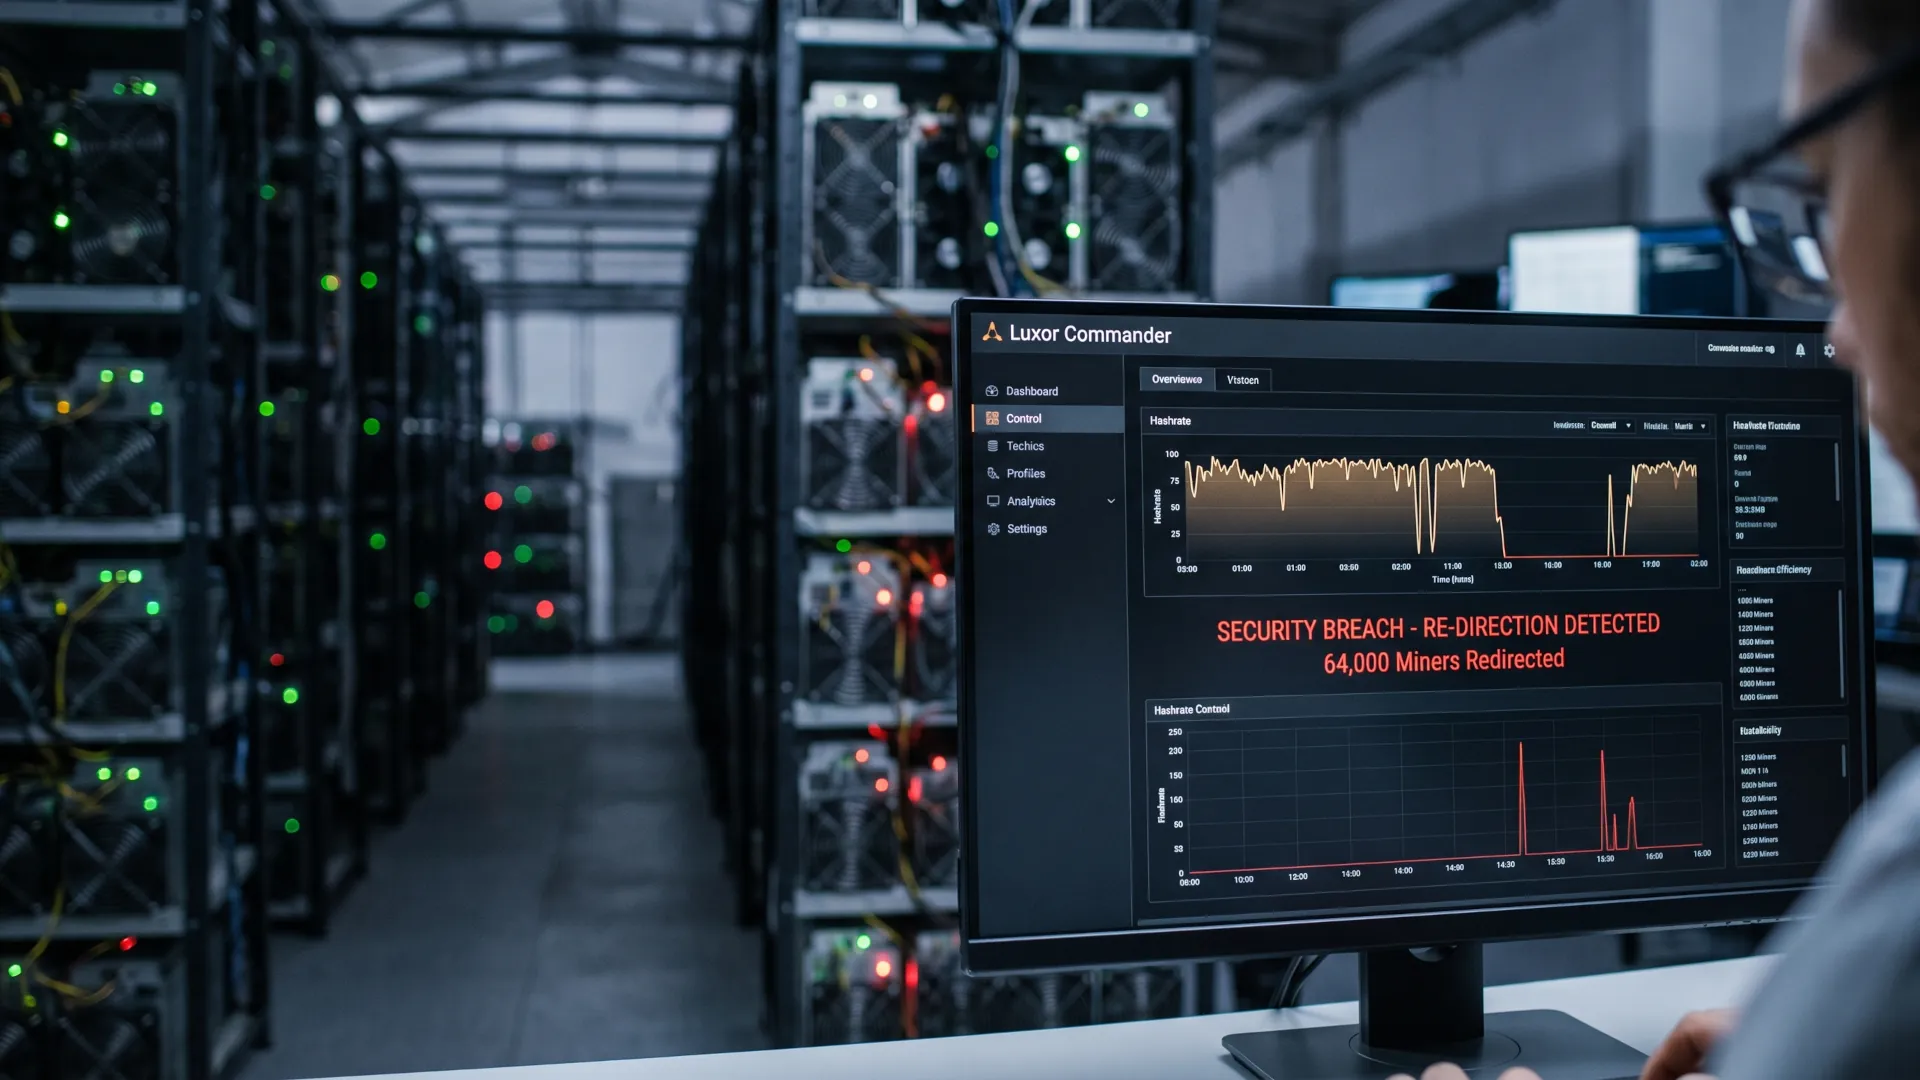
A dashboard for managing mining machines is a boring piece of software until it changes which pool 64,000 rigs point to and nobody notices for hours. Luxor, one of the best-known mining technology companies in the United States, confirmed on November 16, 2026 that its Commander platform suffered a breach that allowed hashrate from more than a dozen customer accounts to be redirected to a different pool.
The company said so in a public message: the redirect stopped being a suspicion when its internal monitoring detected it, they patched it within two hours and promised to compensate customers who lost the redirected power. What remains unclear is how the attacker got in, how long they kept control or how much money was lost in total. Nick Hansen, Luxor's CEO, spoke of a "sophisticated" vector enabled by artificial intelligence and placed the start of the attack at around six in the evening on November 14, Pacific time.
The incident points to a blind spot in the sector that grows with the market. Bitcoin mining is today an industrial infrastructure managed by remote software, with thousands of machines that obey a central dashboard.
The on-chain data says it all
The first warning did not come from Luxor but from CoreX Hosting, another infrastructure provider, which alerted on its X account on November 15 that rigs were being redirected to OCEAN and that the rewards were going to a single bitcoin address. GalaxyMind estimated that the redirect affected some 64,000 machines and 13 exahashes per second since the previous night.
CoinSpect put that figure in context: 13 EH/s represented around 1.5 percent of bitcoin's global hashrate. The OCEAN data confirms only part of the story: the flagged address received three payments totaling 0.24308905 BTC between November 15 and 16. OCEAN's reward system allows work submitted earlier to keep generating payments in later blocks, so the amount does not measure how much the diversion was worth.
CoreX said it restored the machines to their original configuration, isolated the responsible program and considered the incident closed when the hashrate of the suspicious address fell to about 100 petahashes per second. That is a huge drop from the 13 exahashes described at the start, and that gap between the initial and final scope is one of the holes the investigation will have to explain.
The reward figures look small next to the diversion of capacity, and that apparent contradiction has a technical explanation that should be kept separate from the headline before drawing conclusions about the real scope of the attack.
What the account confirms and what it does not
Luxor confirms a breach and confirms that more than a dozen customer accounts had machines pointing to another pool during a limited window. It also confirms that there was no exfiltration of data from its systems, and that it will compensate the diverted hashrate. So far, facts verifiable by the company itself.
What it does not confirm is who was responsible, the method of entry or the amount of the damage. That the company's director describes the attack as an AI-enabled vector is a claim by one party, not a technical conclusion reproduced by a third party. The sector has spent months attributing an increase in malicious activity to AI, and that narrative also serves a commercial purpose.
The difference between the two versions is not a detail. If the attacker used a compromised customer account, responsibility is shared between the provider and the customer. If the flaw was in the platform, the provider bears almost all of it. The public investigation will say which of the two happened, and until then the incident resembles others that ended in silence.
The case resembles that of N-able and its 33 zero-days, where an administration tool with privileges over thousands of machines became the most profitable point in the ecosystem, although here the asset was not data. What was stolen here was computing capacity, which turns into money every ten minutes and leaves no trace of personal data.
The detail of the chosen pool also deserves a note, because OCEAN is not accused of anything and appears in the account only as the recipient of work that other rigs submitted without knowing it.
Target: a mining control dashboard
Mining bitcoin is a race on energy costs. A small or medium-sized miner buys machines, connects them to a pool and gets paid according to the work contributed. If someone changes where the work goes, the owner keeps paying for electricity while the reward arrives in another wallet, and how long it takes to detect depends on how many times they check their dashboard.
The diversion is paid for in electricity and lost in rewards, two different currencies that are rarely looked at in the same spreadsheet and that leave the operator feeling they worked for free.
That window of hours is enough to move 13 exahashes to a controlled pool. The pool chosen in this case, OCEAN, is legitimate and is not accused of anything: the problem is that receiving someone else's work without consent makes its operator the recipient of payments that are not theirs. The traceability of the flagged address suggests the attacker did not hide the collection too much.
Mining has a characteristic that sets it apart from other sectors: the rigs accept configuration orders without human authentication. Firmware that obeys the dashboard is fast and convenient, and it is also the perfect scenario for a mass attack.
That dependence on the dashboard concentrates risk in a single software provider, which becomes as critical as the electrical substation that powers the facility and that nobody checks until it shuts down.
The mining dashboard has become the link nobody audits, and the attacker knows it. The useful question is not who did it, but what can be verified without trusting the tool.
What should an operator do after this warning?
The first check is the pool configuration on each rig, not on the dashboard. The operators who discovered the change saw it on the machines, and that is the only place where the truth does not depend on the compromised tool. Comparing the destination of each group of miners with the expected configuration is a manual task that should be automated independently of the dashboard.
The second is to review the dashboard credentials and customer accounts with write permissions. If access came through a customer session, key rotation and revocation of active sessions should be done the same afternoon. Luxor says it patched within two hours, and has not detailed exactly what it closed.
The third is to calculate the real loss using the pool's records. An operator who paid for electricity for eight hours for work they were not paid for has a concrete loss, and claiming it requires the list of blocks and payments, not a hashrate estimate. Luxor committed to compensating, and customers would do well to keep that documentation while the promise holds.
It is also worth watching the price of hashrate over the following days. A massive diversion moves the difficulty and profitability of all participants, and that footprint is easier to follow than that of the wallet collecting the payments.
What the incident says about mining software
Mining has professionalized faster than the security of the tools that manage it. Administration dashboards were designed for a world where the operator was a trusted person with access to the local network, and today they are cloud services with thousands of customers and with permissions to change where the money goes.
The lesson matches that of other sectors that outsourced administration. The software provider concentrates trust, and that trust has a price that nobody pays until there is an incident. When it is paid, it usually costs more than the software of all its customers combined.
For the reader who operates miners, the practical conclusion is uncomfortable. The configuration of your infrastructure must be verifiable without depending on the provider, and the money it generates must be auditable without their permission. That separation of functions is the same one banking learned a century ago.