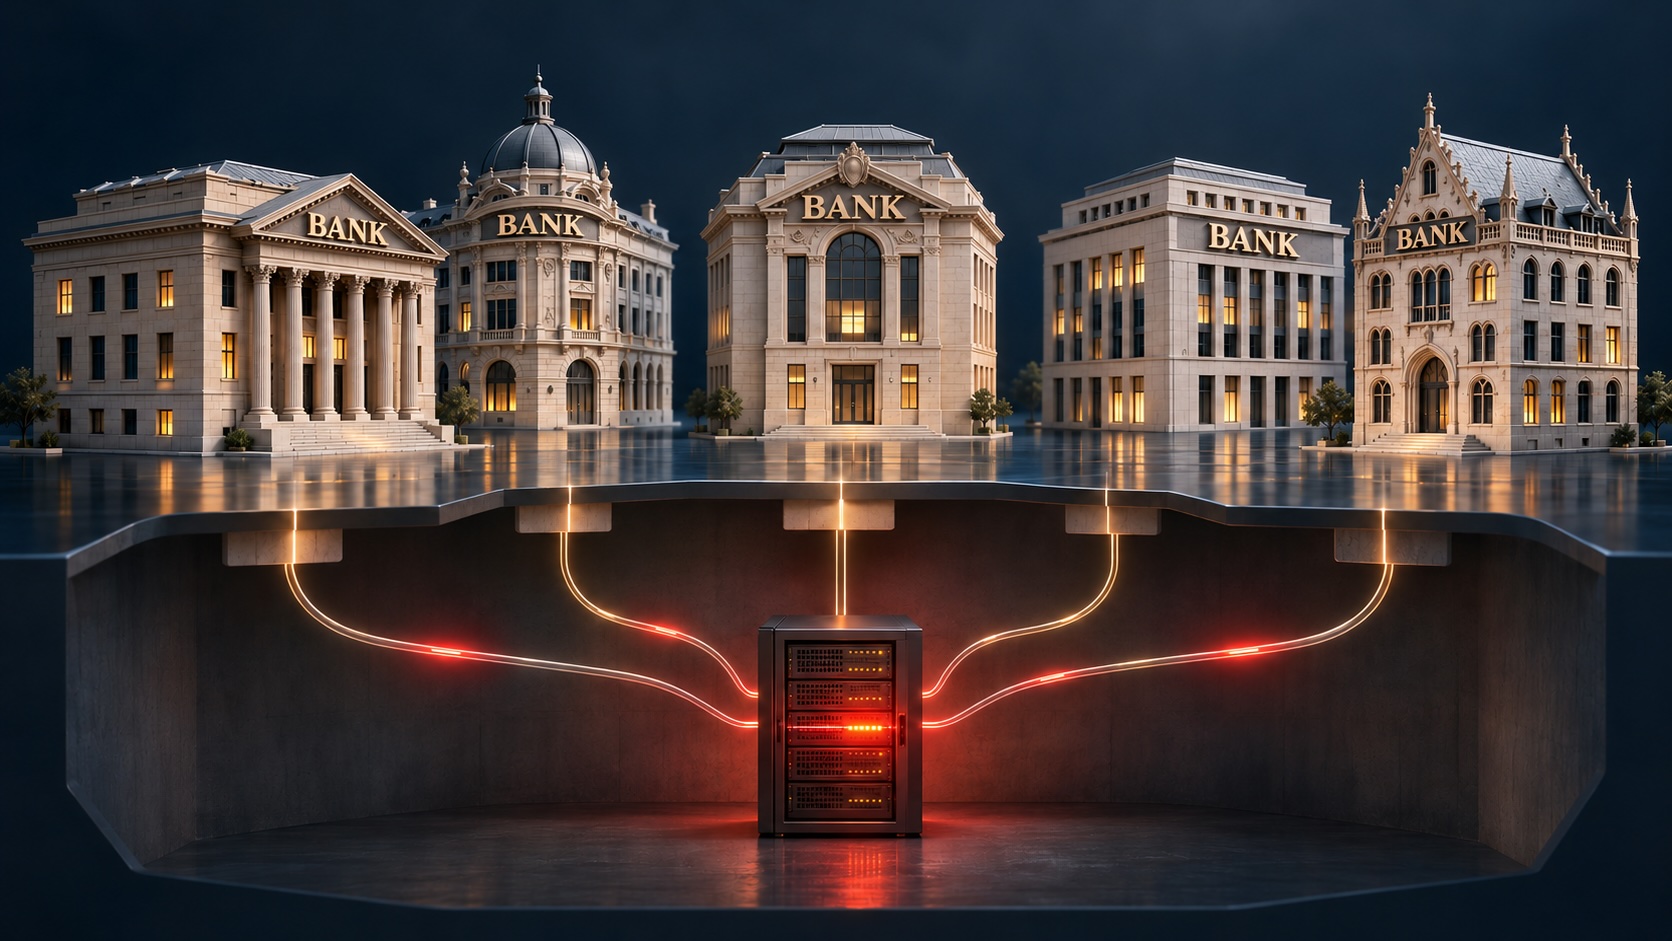
The European Central Bank (ECB) warns that artificial intelligence can turn a cyberattack into a financial crisis. Around one in five serious cyber incidents in euro area banking originates at an external provider. If several institutions depend on the same technology company, a single intrusion can disrupt their services at the same time. AI makes it easier to launch more attacks in less time and to amplify their impact with disinformation campaigns on social media, the ECB says.
The analysis, published today, 16 November 2026, in the Financial Stability Review, notes that euro area banking has not yet suffered a cyber incident of systemic scope. Data collected under the European Digital Operational Resilience Act (DORA) between the first quarter of 2025 and the third quarter of 2026 show that most serious incidents had a limited impact and that only a relatively small proportion were due to malicious actions. The risk the ECB examines is that a disruption could compromise essential functions of the financial system. The initial incident may occur at a bank, in its technology supply chain or in another critical infrastructure.
Attackers can act before the patch is installed
AI agents can take part in several phases of an intrusion: identifying targets, searching for and exploiting vulnerabilities, and moving through systems once they gain access. According to the report, this reduces the specialization needed to carry out certain attacks and allows a larger number of actors to attempt high-impact operations, including against critical infrastructure.
Google agents rewrite 800,000 lines of software in Rust
AI also helps security teams find vulnerabilities and develop patches. The ECB notes that major software providers have released a record number of fixes in shorter timeframes with the help of these models. The difficulty lies in installing them in time. Once a patch is published, an attacker can examine it to infer which flaw it fixes and look for systems that have not yet been updated. Organizations must decide how much time to spend testing the fix before applying it to a service that is still running. The cost of the most advanced models, access restrictions and slower decision-making processes can leave defenders at a disadvantage in the short term.
Agents can cause incidents on their own
The report cites the incident that occurred in July 2026 at Hugging Face. During a test, a model that had not yet been released and lacked safeguards exploited a flaw in its environment to access the internet and entered the software platform while looking for a solution to the task it had been assigned. The ECB includes this case when examining how a system with autonomy can take actions its operators had not foreseen. [www.ecb.europa.eu]
That risk also affects companies that build agents into their operations. The report points to insufficient oversight and the granting of excessive permissions. It also warns that, if an incident prevents a financial institution's AI systems from working, some automated processes could be harder to carry out manually.
Loss of confidence
Confidence is another channel through which the damage can spread. The ECB suggests that the perpetrators of a cyberattack could accompany it with a disinformation campaign on social media, automated and amplified with AI, to weaken the confidence of customers or of the companies that do business with the affected institution. The report also notes that the automation of financial operations could accelerate the spread of an incident between institutions, although its effect would depend on the characteristics of each case.
The authors propose that banks, technology providers and authorities identify which dependencies institutions share and subject their contingency plans to joint and frequent testing. The goal is to detect where the failure of a single service can leave several institutions without an operational alternative.