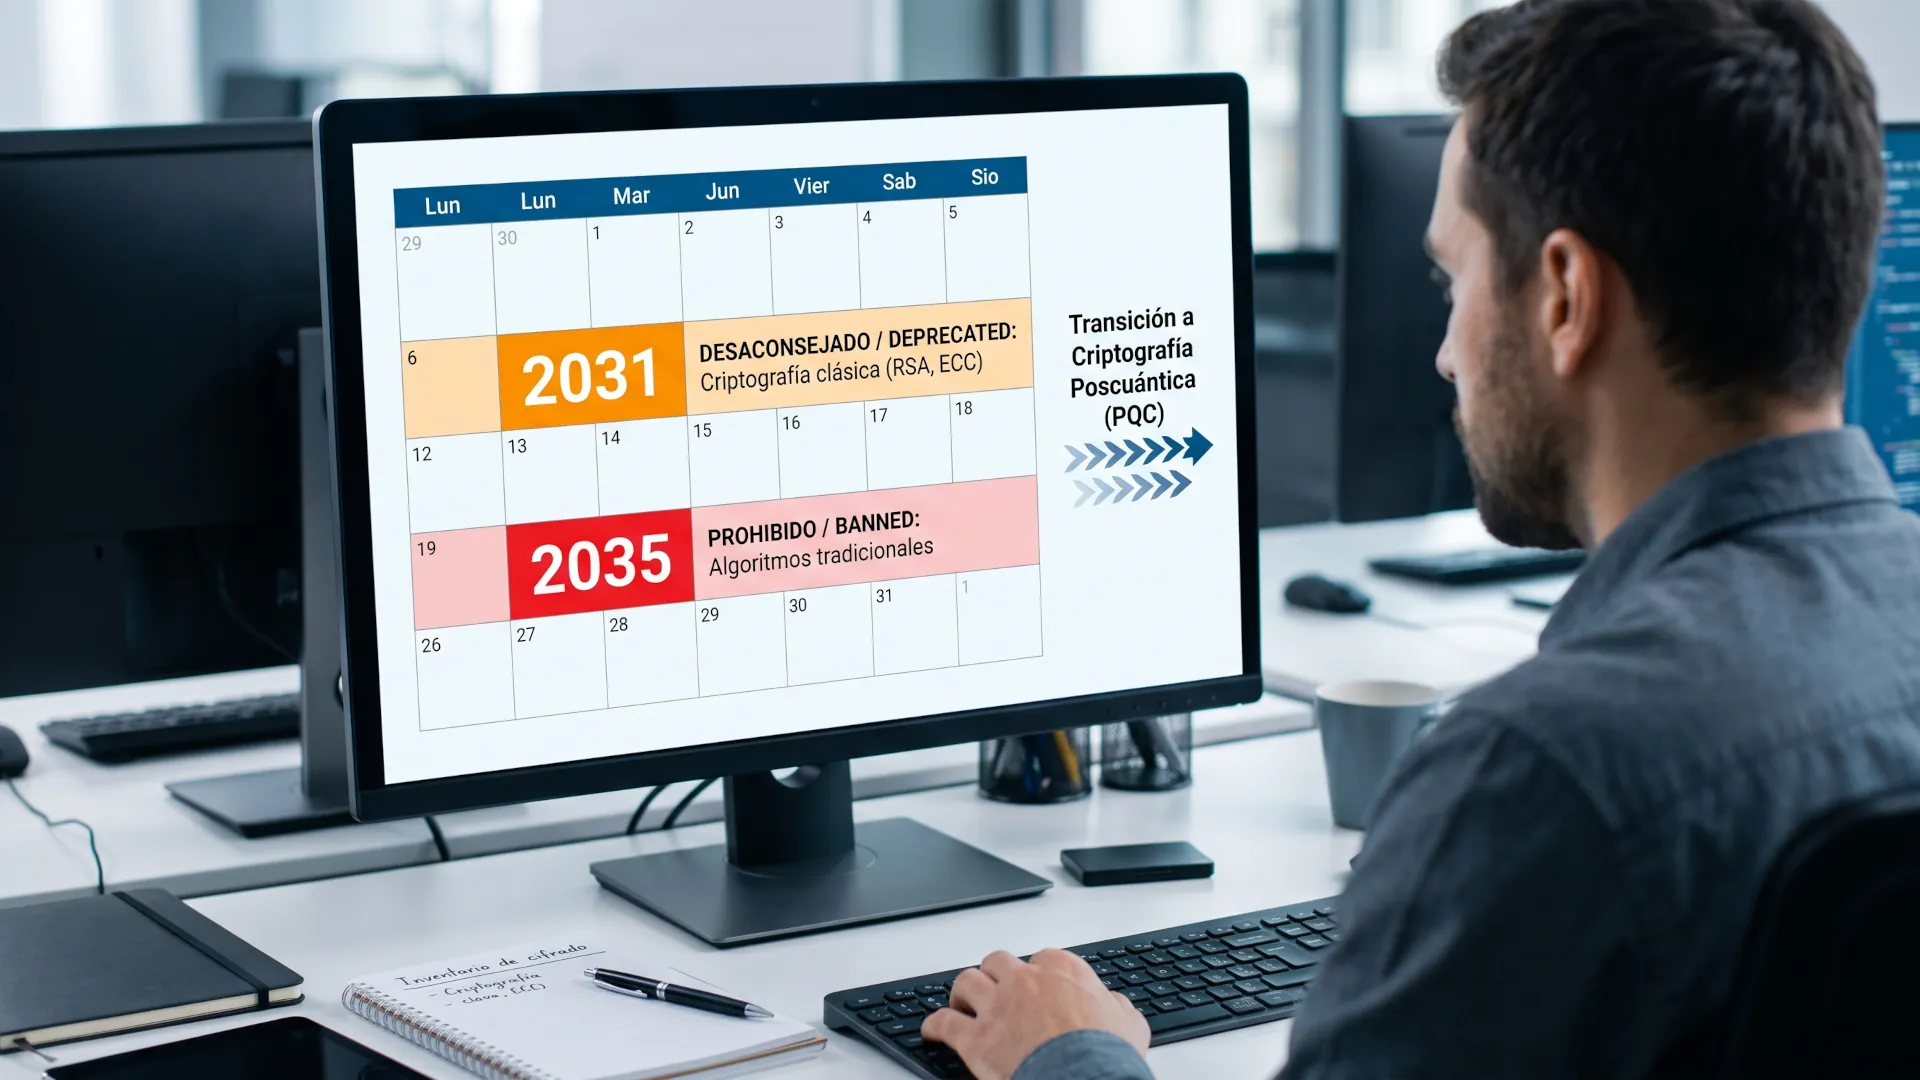
A TLS certificate issued this week may still be standing when the timetable NIST has just published is already out of date. The US agency closed on October 27 the final version of its guide to the transition to post-quantum cryptography, and the text sets two deadlines: the public-key algorithms in use today are discouraged from 2031 and prohibited after 2035. The list includes RSA and elliptic-curve cryptography in all its approved sizes, which is what certification authorities and firmware updates sign with.
The timetable is not a law, and it does not arrive on its own either. The White House had tightened it in June with an executive order requiring the most sensitive federal systems to migrate key exchange by December 31, 2030, and digital signatures by December 31, 2031, and the final report aligns with those two dates. Outside the federal sphere it functions as guidance, although vendors that sell to the Government will feel the effect through contracts sooner than their internal roadmaps suggest. Hence the date worth noting is not 2035 but 2031, and the outstanding work looks more like drawing up an inventory of what an organization encrypts and signs than like choosing an algorithm.
A draft that dates back to 2024
The public draft was released on November 12, 2024, and the final version withdrew it on the same day it was published, two years later. That text only advised against 112-bit parameters, including RSA-2048 and the P-224 curve, while P-256, RSA-3072 and Ed25519 remained acceptable until 2035 with no intermediate step. The final report lumps together all approved sizes: RSA and ECDSA signatures from 112 bits, EdDSA from 128, and key establishment with Diffie-Hellman, MQV or RSA.
Only one of the report's three statuses prohibits something. Deprecated allows continued use of the algorithm if the data owner examines the risk and decides to proceed, and legacy use is reserved for decrypting old data or verifying signatures already issued.
Comments on the draft had already flagged the gap. NIST received 25 written responses before the deadline closed in January 2025, with manufacturers such as Infineon, Intel and Thales among the signatories, and several noted that no one migrates while the algorithm remains acceptable. The result is a notice five years before the cutoff, not a few months before, and P-256 appears in the deprecated column from 1 January 2031.
An inventory problem, not an algorithm problem
Swapping RSA for ML-KEM sounds like replacing a library and re-testing. The report frames it differently: before touching anything you have to know what is running, and that question has an uncomfortable answer in almost any mid-sized company. Cryptography lives in the load balancer, in the VPN, in the server's security module, in the library someone compiled in 2019 and in the firmware of a network printer.
Dustin Moody, a mathematician at NIST and head of the post-quantum standardization project, summed up the difficulty in the presentation: "We understand that there is no one-size-fits-all strategy for all use cases."
Inventories are the real bottleneck. The GAO reviewed the 24 federal agencies and concluded that none had fully covered the three preparatory practices it evaluated, including the prioritized inventory of systems with vulnerable cryptography. The report, reissued on 14 October, includes 89 recommendations to 23 agencies and points to the lack of processes for building those inventories.
Meanwhile, public debate remains focused on the day a quantum computer breaks something, as happened with Google's quantum advance that revived the discussion about Bitcoin's security. The NIST timetable says the countdown began earlier, at the moment someone copied the traffic and stored it on a disk.
Why can a 2026 key still sign in 2036?
There is one case that is more troubling than any other. A certificate authority generates its classic root key this year with the idea of issuing TLS certificates for a decade, and that key is born valid and dies discouraged: after 2035 it cannot sign new certificates under NIST standards.
The lifecycle governs. A company can renew its certificate every 90 days and still carry a chain that ends in a long-term classic signature, because trust is inherited downward and is not renewed piece by piece. The executive order adds its own date for federal agencies, with mandatory support for TLS 1.3 no later than January 2, 2030, and the report names the protocol as an early priority.
The hybrid path exists and NIST accepts it. A scheme that combines a classic curve with ML-KEM can be validated under FIPS 140 as long as one of the inputs comes from an approved scheme, and the agency recommends ML-KEM-768 by default. The alternative chosen as the second encapsulation mechanism is HQC, which still lacks a finalized standard.
None of that replaces the hard part. A compromised certificate forces revocation and reissuance, and the episode of the compromised eMudhra TLS certificates showed how quickly an issuance failure becomes a problem for the entire chain. With larger post-quantum signatures, each link weighs more in a browser handshake.
The dates to note
The phased timetable reads better as a table, with one idea in mind: harvest now and decrypt later means an adversary copies today the encrypted traffic it cannot open and stores it until it has a machine capable of breaking it. If that data must remain secret in 2033, the date that matters to its owner is not 2035.
| Date |
What happens |
Who it affects |
| October 27, 2026 |
Final version of the report |
Guidance for the industry; binding on the U.S. public sector |
| January 2, 2030 |
Mandatory TLS 1.3 support |
Federal agencies and vendors |
| December 31, 2030 |
Post-quantum keys in high-impact systems |
Agencies and contractors |
| January 1, 2031 |
RSA and elliptic curves become discouraged |
Any system that keeps using them |
| December 31, 2031 |
Post-quantum signatures in high-impact systems |
Agencies and contractors |
| After 2035 |
Classical algorithms prohibited |
All, under NIST standards |
The useful reading is that 2030 and 2035 are exit dates, not arrival dates. The report recalls that previous cryptographic transitions took between 10 and 20 years, and these leave four and nine years ahead. Anyone who starts migrating in 2029 will not make the cutoff with the least critical systems.
Outside the United States the calendar is also moving
On October 23, the ITU announced the X.1711 standard, the first international standard dedicated to quantum key distribution protocols, a system that distributes keys over a physical channel instead of relying on mathematical difficulty. The text does not choose a specific protocol: it describes the architecture and the common flow, and leaves the protection profiles for equipment in the hands of ETSI and ISO/IEC.
Vietnam opened for comment on October 17 three draft national standards and a roadmap with milestones in 2027, 2030, 2033 and 2035 to bring 100% of its critical systems to post-quantum cryptography. The drafts are HB-PQSign, a hash-based signature developed in the country, alongside the national versions of ML-KEM and ML-DSA. The plan reserves quantum distribution for specific networks and leaves post-quantum as the general solution, the same split the ITU makes.
What a management committee should put on the list
The first task is not choosing ML-KEM or deciding whether hybrid mode is advisable. It is knowing how many systems sign something that must remain verifiable in 2036, and how many store data that must remain secret in 2033. Those two questions organize the work better than any official date and expose the equipment that cannot be migrated and will have to be replaced.
There is a margin that looks comfortable and is not. The certificates, security modules and firmware manufactured today will outlive the cutoff, and none of them is changed in a weekend. The 2031 date does not say when you have to finish; it says when not having started begins to cost dearly.